confaudit
Configuration compliance for network teams
Who it’s for
Network engineers at MSPs and mid-size companies preparing for audits, or checking that their configuration standards hold.
What it does
Works from backups
Reads RANCID and Oxidized backup folders. It never logs in to a device.
Mapped to frameworks
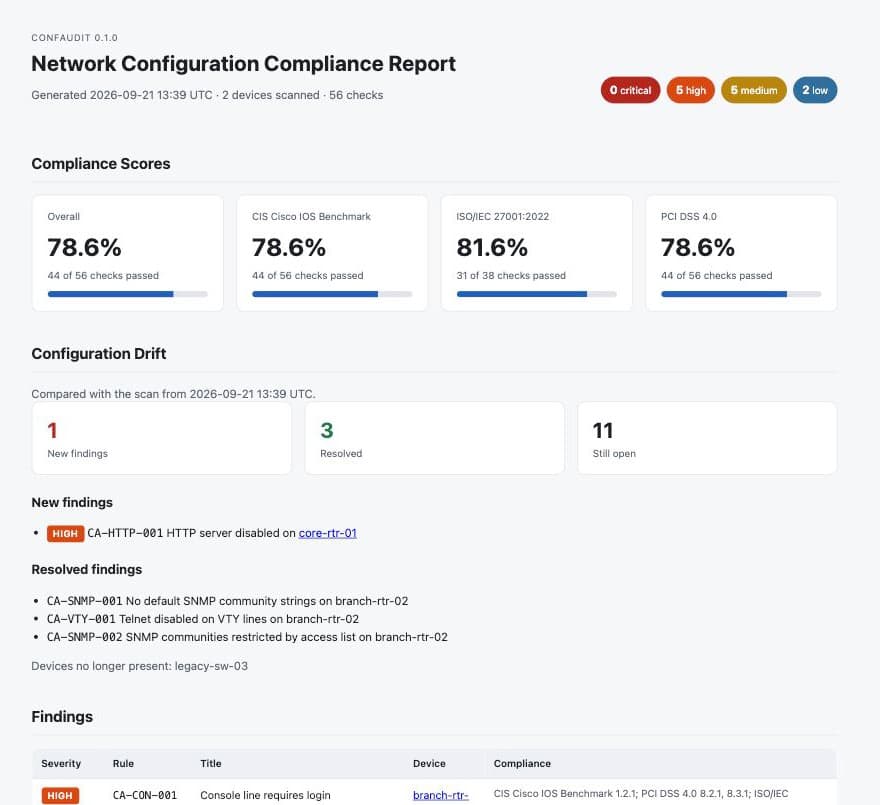
Rules mapped to the CIS Cisco IOS Benchmark, PCI DSS 4.0 and ISO/IEC 27001:2022, with scores per framework.
A fix for every finding
Every finding comes with the commands that fix it on that device.
Drift between runs
New, resolved and still-open findings since the last run, so you see whether things are getting better.
How it works
Point it at your backups
A folder of configurations, from RANCID, Oxidized or anything else.
Rules run
Each device is checked against the built-in rules and any you add.
Read the report
HTML, Markdown, JSON or a PDF for auditors, with scores, findings and fixes.
Run it again
Watched folders rerun the checks as configurations change, and the report shows what drifted.
See it on your own network.
We’ll walk you through it with data that looks like yours, and tell you honestly whether it fits.